What Is Agentic AI? Architecture, Use Cases, Risks, and a Practical Deployment Framework
Quick answer: Agentic AI is an AI system that receives a goal, selects from a bounded set of permitted actions (tools), observes results, updates state, and repeats until a defined stopping condition. This article is for product managers, engineering leads, security owners, and operations teams planning a production-ready agentic AI deployment.
Byline: Wizora Studio — updated 2026-08-26
Agentic AI, in plain English
Agentic AI combines a decision loop with tool use. A useful definition includes five parts:
- Goal: the objective the system pursues.
- Bounded tools: APIs, search, databases, email, calendars or narrow internal functions the agent is permitted to call.
- Decision loop: the model evaluates context, picks the next action, executes a tool, observes the result, and repeats.
- State: a record of prior actions, tool results and relevant context.
- Stopping or escalation rules: success, budget limit, handoff to a person, or an error condition.
If a system only generates text from a prompt it is generative AI but not necessarily agentic. If every action and branch is fixed in advance it is workflow automation. The practical distinction is where and how decision-making happens.
How agentic AI works: the loop and a concrete example
A production agent typically follows this loop:
- Receive and normalize the task (message, form, ticket).
- Load permitted context (CRM records, policies) with proper authorization.
- Model selects a typed tool and prepares arguments.
- Validate arguments deterministically (schema, permissions, budgets).
- Execute tool and observe structured result.
- Update state (actions, cost, remaining objective).
- Decide: stop, retry, continue, or escalate to a person.
Concrete example: inbound sales qualification (end-to-end)
- Normalize input: parse contact, consent, message text.
- Retrieve customer and account data with tenant-aware filters (no duplicates).
- Apply deterministic exclusions (unsupported regions, prohibited industries).
- Summarize inquiry, identify missing fields, and recommend a qualification status with evidence links.
- Draft a reply and, if required, open an approval request to a salesperson.
- On approval, write the result and evidence to the CRM with idempotency keys.
- On dependency failure (CRM timeout), record the partial outcome, notify the owner, and retry safely.
Agentic AI architecture and core components
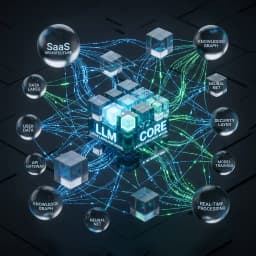
Don't center the diagram solely on the LLM. The surrounding control plane is the product.
- Task & identity layer: authenticated identity, tenancy, and accountable process owner — authorization belongs here, not in the prompt.
- Orchestrator: manages loop, tool registry, state, retries, timeouts and stopping conditions.
- Model gateway: centralizes model selection, rate limits, fallbacks and logging.
- Context & retrieval: enforce permissions at retrieval time; vectors are not an authorization system.
- Tool layer: narrow, typed, reversible actions with idempotency keys.
- Policy & approval: gates based on impact (value, sensitivity, novelty), not model confidence.
- Observability: trace the full trajectory: tool selection, intermediate state, cost, latency and failure recovery.
When to use an agent — and when not to
Use an agent when the path materially changes case-by-case and the system must select tools or sequence work based on context. Prefer deterministic workflow automation when the path can be specified in advance. Many dependable systems combine both: a deterministic workflow surrounds a flexible decision step.
Avoid or constrain agents when the correct path is rules-based, actions are irreversible and high-cost, required systems cannot expose narrow permissions, regulatory duties demand a human decision, or volume doesn't justify complexity.
Implementation checklist and production-readiness guidance
Before deployment, verify each item below:
- Outcome and metrics: one measurable business outcome (e.g., first-response time, exceptions per 1,000 requests).
- Ownership: named process owner, technical owner, security contact and escalation rota.
- Permissions mapping: identities, tenants, tool scopes, write actions and retention rules enforced outside the model.
- Deterministic validation: schema checks, business-rule engines, monetary caps, allowed recipients, and idempotency.
- Normal & abnormal scenarios: representative and adversarial test set including dependency failures and hostile inputs.
- Observability & audit trail: log full decision traces, tool inputs/outputs, costs and escalation reasons.
- Rollout plan: small cohort release, restricted actions, monitoring dashboards and rollback playbook.
- Governance: approval gates, retention policy, and a plan for periodic evaluation after model or API changes.
Risks, limitations, and security considerations
- Prompt injection: treat retrieved text as untrusted data and separate instructions from content.
- Excessive agency: avoid broad credentials; prefer prepare-then-approve for consequential writes.
- Cross-tenant leakage: enforce tenant filters in retrieval, caches and logs.
- Sensitive-data leakage: redact or tokenize secrets; do not place credentials in prompts.
- Compounding errors: validate intermediate results, cap actions, and require fresh evidence before high-impact steps.
Cost, latency, and reliability trade-offs
Measure cost per completed business task. Route work sensibly: deterministic code for known checks, small models for narrow classification, stronger models for complex planning. Design for asynchronous execution of long-running dependencies, show progress to users, and avoid naive retries that duplicate side effects.
Best practices, governance, and human oversight
- Earn autonomy with evidence: start at low autonomy levels and expand only with measured success.
- Design approvals by action impact, not model confidence.
- Keep an explicit exception queue with owners and resolution state — a transcript is not an operations queue.
- Version prompts, models, tools and policies together and hold held-out cases to detect regressions.
Production checklist (quick)
- One measurable outcome and baseline.
- Process and technical owners assigned.
- Permission model enforced outside the LLM.
- Deterministic validators for tool calls.
- Idempotency keys on write operations.
- Observability for full trajectories and cost metrics.
- Small cohort rollout, monitoring and rollback plan.
Technical & accessibility notes
Ensure server-rendered text for SEO, provide meaningful image alt text where used, and include structured logs and audit trails for later evaluation. Design UI status updates with reduced-motion options and clear progress indicators for asynchronous tasks.
Frequently asked questions
What is the difference between agentic AI and generative AI?
Generative AI produces content. Agentic AI adds a control loop and tool use: it can choose actions, execute tools, observe results and continue toward a goal.
Can an AI agent operate without human approval?
Yes for bounded, low-risk actions when permissions, monitoring and recovery exist. High-impact steps should be approval-gated.
How should businesses test agents?
Score the full run on representative and adversarial cases: goal understanding, evidence retrieval, tool-selection accuracy, validation failures, escalation behavior and final usefulness.
Conclusion and next steps
Agentic AI is powerful when a process requires contextual choice. The model may decide the next step, but the organization decides tools, permissions, evidence, budgets, approval points and acceptable failure rates. The practical default: pick one bounded task, start at low autonomy, surround the model with deterministic controls, monitor full trajectories, and expand responsibility only with evidence.
If you want help mapping a real task into a safe production agent, Wizora Studio offers custom agentic AI services and implementation support. Start the conversation with a small, concrete workflow and sample inputs: see our AI automation services at /services/ai-automation or request a project conversation at /contact. View examples of our work at /work.
References and editorial evidence
• Wizora Studio — What Is Agentic AI (this page) • OpenAI — A Practical Guide to Building AI Agents • NIST — AI Risk Management Framework • Anthropic — Measuring AI Agent Autonomy in Practice • European Commission — Navigating the AI Act
Editorial note: operational scenarios are composite examples for illustration, not claimed client case studies. Legal and regulatory references are for context, not legal advice.